Techdirt lawsuit settled

Back in 2017 Techdirt wrote a series of articles about Shiva Ayyadura. Shiva claims he invented email. (narrator voice: he didn’t). I wrote about the lawsuit when it was dismissed on First Amendment grounds. The parties cross appealed, and have been in settlement talks for 18 months.

According to Techdirt, the non-monetary settlement they agreed to is that all the articles in dispute will have a link to a statement published by Shiva.

You may wonder how it could possibly take 18 months to negotiate a settlement about adding links to old articles — and, indeed, I wonder that myself. The entire process has been quite a pain for us. I cannot and would not describe this result as a victory, because this has been nearly two and a half years of wasted time, effort, resources, attention and money just to defend our right to report on a public figure and explain to the world that we do not believe his claims to have invented email are correct, based on reams of evidence.


Related Posts

Internet security is national security?

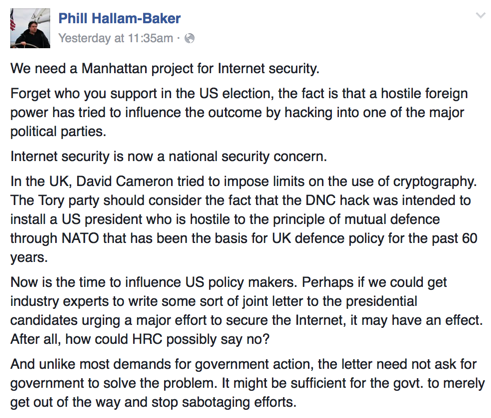
This popped up on my FB feed yesterday.
2016-08-04_16-27-53
What say you? Do we need to create a major effort to improve online security? What challenges do you see to making it work?
Edit: After I published this, I found an article stating that 3.7 million people had their personal health information compromised in a recent attack.

Read More

Happy New Year!

Well, we mostly survived 2016. A year ago I was making predictions about how 2016 would be the year of email security. I was thinking of things like TLS and authentication and access to the inbox. It wasn’t out of the question, Gmail said they’d be turning on p=reject sometime mid-year. They also were suggesting that they would be putting more value on messages that aligned, even in the absence of a DMARC signature. The first still hasn’t happened, and the second doesn’t appear to be in place, either.
DataSecurity_Illustration
That doesn’t mean email security wasn’t a hot topic in 2016. In fact, the use of a private email server was a major topic during the US elections. We also had spear-phishing play a major role in the compromise of campaign systems. I didn’t talk much about that here when it happened, but news reports make it clear that Chairman Podesta and others were targeted for compromise. The NY Times has a more in depth article with broader context around the attacks and how emails were used to infiltrate a major political party.
The irony is with all the time spent talking about how insecure the private server was, that server wasn’t compromised. Instead, the compromise was at Gmail.
We all need to pay attention to our email and how we use it. It also means when we’re sending bulk and marketing email we need to consider the private and personal information we’re putting in messages. Do you send PII? Is there a way you don’t have to? What can we do to protect our brand and our users?
It’s not just bulk email we need to think about, either. Personal email can contain PII, or personal information. A common saying among some of my security friends is “never put in email anything you wouldn’t want to see on the front page of the Washington Post or NY Times.” That’s an easy thing to say, but the convenience of email makes it easy to share information that we may not want on the front page of either paper. Many of us aren’t actually targets of malicious activity so we don’t have to worry about being targeted the way elected and other officials are. But that doesn’t mean we are not at risk. It just means we’re at less risk than others.
Email is a frequent vector for malicious actors to access computers. Most, if not all of the major breeches in the last few years have started with a phishing attack of some sort. The attacks are planned out and sophisticated. This is not going to get better. The phishers are smart and plan the attacks.  We also need to be more personally aware of security given the current political climate. We need to take steps to protect ourselves more than we have in the past.
Security is more important than ever and we all need to protect ourselves.

Read More
The perfect email

More and more I’m moving away from consulting on technical setup issues as the solution to delivery problems. Delivery is not about the technical perfection of a message. Spammers get the technical right all the time. No, instead, delivery is about sending messages the user wants. While looking for something on the blog I found an old post from 2011 that’s still relevant today. In fact, I’d say it’s even more relevant today than it was when I wrote it 5 years ago.
authenticated
Email is a fluid and ever changing landscape of things to do and not do.
Over the years my clients have frequently asked me to look at their technical setup and make sure that how they send mail complies with best practices. Previously, this was a good way to improve delivery. Spamware was pretty sloppy and blocking for somewhat minor technical problems was a great way to block a lot of spam.
More recently filter maintainers have been able to look at more than simple technical issues. They can identify how a recipient interacts with the mail. They can look at broad patterns, including scanning the webpages an email links to.
In short, email filters are very sophisticated and really do measure “wanted” versus “unwanted” down to the individual subscriber levels.
I will happily do technology audits for clients. But getting the technology right isn’t sufficient to get good delivery. What you really need to consider is: am I sending email that the recipient wants? You can absolutely get away with sloppy technology and have great inbox delivery as long as you are actually sending mail your recipients want to receive.
The perfect email is no longer measured in how perfectly correct the technology is. The perfect email is now measured by how perfect it is for the recipient.

Read More