Security, safety and the cavalry

In some ways it’s been really hard to focus on email for the last few months. There are so many more important issues in the world. Terrorism, Brexit, the US elections compromised by a foreign government, nuclear threats from multiple countries, the repeal of ACA, mass deportations and ICE raids here in the US.  I find myself thinking about what to blog. Then I glance at the news and wonder if there’s any value in another blog post about deliverability.
Generally I’ve tried to keep politics and world events mostly off the blog. But sometimes events are such that I need to talk about them.
Last October I had the chance to speak at the Email Innovations Summit in London. Steve and I took the chance to spend some time doing tourist things in London – including a photo walk along the Thames.
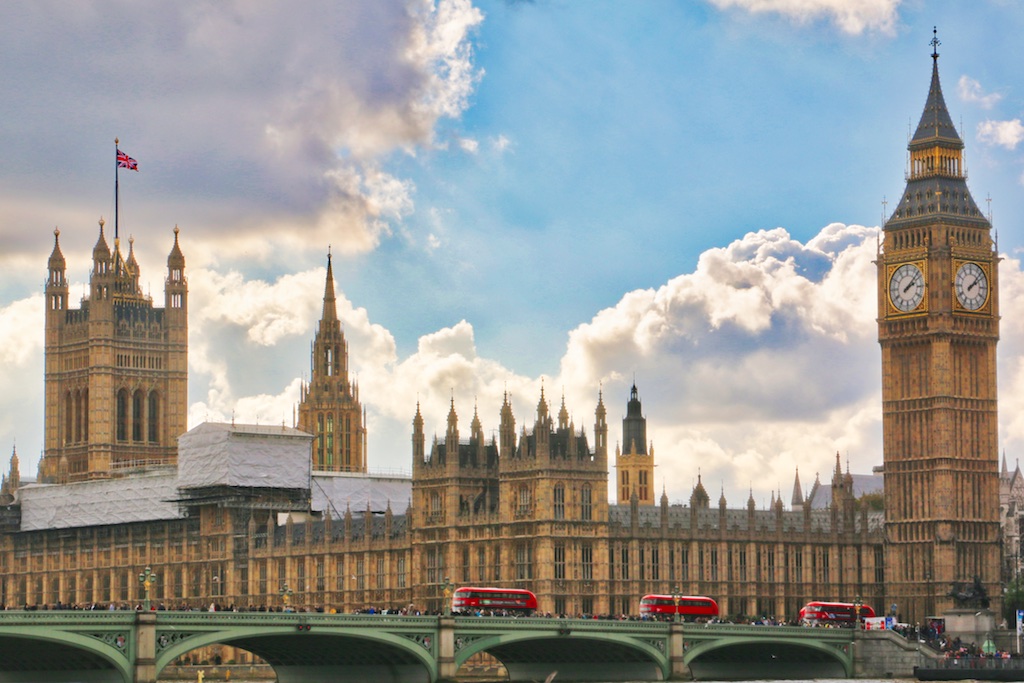
As an American I’m always a little surprised by the security in London. I grew up a few miles outside of DC. I could talk about prohibited airspace and security measures before I was 10. London is so much more open than even the DC of my youth. The surprise there is that London has been a much bigger target and attacked more than any city in the US.
The last few times we were in London I noticed a bit more visible security. In 2013 it was armed security walking through Tube stations. Last year it was Underground trains that were one long car. They were a bit weird and visually disconcerting. The part that really made me think, though, was this was a way to stop people hiding explosives between cars and to facilitate evacuations if something happened.
Last night Steve and I were talking and I mentioned the attack in London didn’t seem like terrorism to me. And it didn’t, not really. He then pointed out that explosives and guns are difficult to come by in the UK and this was classic terrorism. Oh. Sometimes our cultural differences come out in the strangest places.
Thinking about bigger issues like this make it hard to focus on email. There’s a regularly shared joke in deliverability, “There’s no such thing as a deliverability emergency.” And there isn’t, not really. Yes, even if a whole range of IPs is listed on Spamhaus, it’s still not an emergency and there’s no fast response team to deal with it.
There are abuse issues that are higher stakes than getting to the inbox. Child abuse materials. Harassment. Privacy issues. Terror threats. Every online services company, particularly the social media companies, have to deal with these kinds of things. Many of them are dealing poorly. Others have employees who are doing their best, but lack the tools, support, and training to do it well. Many companies don’t understand why they need to police their customer base.
The reality is, though, that abuse on the net (as opposed to abuse of the net) is a huge issue that needs to be dealt with. These are not small issues. The Internet is global and there’s no internet police. Law enforcement in different jurisdictions have to work together with technology experts to address crime and harassment on the internet.
It may surprise you to hear that the people who create spam filters and try and protect your inbox are the same people who fight crime on the internet. Spam and email are a vital part of online crime, so it falls on the abuse team to work with and educate law enforcement about tracing the source of email. The people you never see in ops, and abuse and support are vital to protecting folks online.
During the closing talk at MAAWG the chair was discussing how we can protect our online spaces. He stated “There is no cavalry; no second wave. It’s us or no one.” That’s a huge thing. My friends and colleagues are the people who stand protecting users online. It feels like a huge burden, but it’s something we can do to make the world a better and safer place.


Related Posts

Engagement, Engagement, Engagement

I saw a headline today:
New Research from Return Path Shows Strong Correlation Between Subscriber Engagement and Spam Placement
I have to admit, my first reaction was “Uh, Yeah.” But then I realized that there are some email marketers who do not believe engagement is important for email deliverability. This is exactly the report they need to read. It lays out the factors that ISPs look at to determine if email is wanted by the users. Senders have to deal with vague metrics like opens and clicks, but the ISPs have access to user behavior. ISPs can see if mail is replied to, or forwarded or deleted without reading. They monitor if a user hits “this-is-spam” or moves the message to their junk folder. All of these things are signals about what the users want and don’t want.
Still, there are the folks who will continue to deny engagement is a factor in deliverability. Most of the folks in this group profit based on the number of emails sent. Therefore, any message about decreasing sends hurts their bottom line. These engagement deniers have set out to discredit anyone who suggests that targeting, segmentation or engagement provide for better email delivery and getting emails to the inbox.
There’s another group of deniers who may or may not believe engagement is the key to the inbox, but they don’t care. They have said they will happily suffer with lower inbox delivery if it means they can send more mail. They don’t necessarily want to discredit deliverability, but they really don’t like that deliverability can stop them from sending.
Whether or not you want to believe engagement is a critical factor in reaching your subscribers, it is. Saying it’s not doesn’t change the facts.
There are three things important in deliverability: engagement, engagement, engagement.

Read More

It's not fair

In the delivery space, stuff comes in cycles. We’re currently in a cycle where people are unhappy with spam filters. There are two reasons they’re unhappy: false positives and false negatives.
False positives are emails that the user doesn’t think is spam but goes into the bulk folder anyway.
Fales negatives are emails that the user does thing is spam but is delivered to the inbox.
I’ve sat on multiple calls over the course of my career, with clients and potential clients, where the question I cannot answer comes up. “Why do I still get spam?”
I have a lot of thoughts about this question and what it means for a discussion, how it should be answered and what the next steps are. But it’s important to understand that I, and most of my deliverability colleagues, hate this question. Yet we get it all the time. ISPs get it, too.
A big part of the answer is because spammers spend inordinate amounts of time and money trying to figure out how to break filters. In fact, back in 2006 the FTC fined a company almost a million dollars for using deceptive techniques to try and get into filters. One of the things this company did would be to have folks manually create emails to test filters. Once they found a piece of text that would get into the inbox, they’d spam until the filters caught up. Then, they’d start testing content again to see what would get past the filters. Repeat.
This wasn’t some fly by night company. They had beautiful offices in San Francisco with conference rooms overlooking Treasure Island. They were profitable. They were spammers. Of course, not long after the FTC fined them, they filed bankruptcy and disappeared.
Other spammers create and cultivate vast networks of IP addresses and domains to be used in snowshoeing operations. Still other spammers create criminal acts to hijack reputation of legitimate senders to make it to the inbox.
Why do you still get spam? That’s a bit like asking why people speed or run red lights. You still get spam because spammers invest a lot of money and time into sending you spam. They’re OK with only a small percentage of emails getting through filters, they’ll just make it up in volume.
Spam still exists because spammers still exist.
 

Read More

January 2017: The Month in Email

Between client work and our national political climate, it’s been a very busy month around here and blogging has been light. Things show no sign of slowing down in February, so we’d love to hear from you with questions and suggestions of what you’d most like to see us focus on in our limited blogging time this month. We got a great question about how senders can access their Google Postmaster tools, and I wrote up a guide that you might find useful.

We’re also revisiting some older posts on often-requested topics, such as spamtraps, so feel free to comment below if there are topics you’d like us to address or update. One topic that comes up frequently, both on the blog and in our consulting practice, is about what to do when you’re on a blocklist. I revisited an old-but-still-relevant post on that topic as well.
On the Best Practices front, I wrote about how brands can use multiple channels to connect with customers and prospective customers to promote and enhance email delivery. I also took a moment to look back over 2016 and forward to 2017 in the realm of email security.
I continue to be annoyed by B2B spam, and have started responding to those “requests” for my time directly. Steve also wrote a long post about B2B spam, focusing on how these spammers are using Google and Amazon to try to work around reputation issues.
In case you missed it, I contributed some thoughts to a discussion on 2017 email trends over at Freshmail with my exhortation to “Make 2017 the year you turn deliverability into a KPI.”
I’m also still in the process of completing my 2017 speaking schedule, so I’m looking for any can’t-miss conferences and events you’d recommend. Thanks for keeping in touch!

Read More