Silly Spam

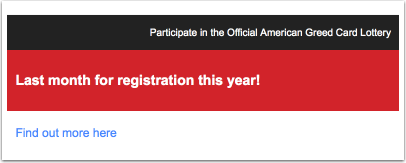
I was cleaning out my inbox over the weekend and found a spam that actually made me laugh.
GreedCardLibrary
Yes, it is spam advertising the “Official Greed[sic] Card Lottery.” It’s been 20 years since I’ve seen one of those!

Live, work and study in the USA
The American Dream Within Reach
50,000 people and their families will get a green card
Simple registration within 5 minutes

Yeah, we’ll get right on that!
 

Related Posts

Spammers, eh?

SpamBoxI’m back from a fun and successful trip to the APSIS Email Marketing Evolved conference. Of course, this means I’m digging out my mailboxes and going through mail I’ve ignored for the past week. It’s amazing how the spam builds up when I’m not tending to it every day.

Read More

September 2015: The month in email

September’s big adventure was our trip to Stockholm, where I gave the keynote address at the APSIS Conference (Look for a wrapup post with beautiful photos of palaces soon!) and had lots of interesting conversations about all things email-related.
Now that we’re back, we’re working with clients as they prepare for the holiday mailing season. We wrote a post on why it’s so important to make sure you’ve optimized your deliverability strategy and resolved any open issues well in advance of your sends. Steve covered some similar territory in his post “Outrunning the Bear”. If you haven’t started planning, start now. If you need some help, give us a call.
In that post, we talked a bit about the increased volumes of both marketing and transactional email during the holiday season, and I did a followup post this week about how transactional email is defined — or not — both by practice and by law. I also wrote a bit about reputation and once again emphasized that sending mail people actually want is really the only strategy that can work in the long term.
While we were gone, I got a lot of spam, including a depressing amount of what I call “legitimate spam” — not just porn and pharmaceuticals, but legitimate companies with appalling address acquisition and sending strategies. I also wrote about spamtraps again (bookmark this post if you need more information on spamtraps, as I linked to several previous discussions we’ve had on the subject) and how we need to start viewing them as symptoms of larger list problems, not something that, once eradicated, means a list is healthy. I also posted about Jan Schaumann’s survey on internet operations, and how this relates to the larger discussions we’ve had on the power of systems administrators to manage mail (see Meri’s excellent post here<).
I wrote about privacy and tracking online and how it’s shifted over the past two decades. With marketers collecting and tracking more and more data, including personally-identifiable information (PII), the risks of organizational doxxing are significant. Moreso than ever before, marketers need to be aware of security issues. On the topic of security and cybercrime, Steve posted about two factor authentication, and how companies might consider providing incentives for customers to adopt this model.

Read More
Your system; your rules

In the late 90s I was reasonably active in the anti-spam community and in trying to protect mailboxes. There were a couple catchphrases that developed as a bit of shorthand for discussions. One of them was “my server, my rules.” The underlying idea was that someone owned the different systems on the internet, and as owners of those systems they had the right to make usage rules for them. These rules can be about what system users can do (AUPs and terms of service) or what about what other people can do (web surfers or email senders).
I think this is still a decent guiding principle in “my network, my rules”. I do believe that network owners can choose what traffic and behavior they will allow on their network. But these days it’s a little different than it was when my dialup was actually a PPP shell account and seeing a URL on a television ad was a major surprise.
But ISPs are not what they once were. They are publicly owned, global companies with billion dollar market caps. The internet isn’t just the playground of college students and researchers, just about anyone in the US can get online – even if they don’t own a computer there is public internet access in many areas. Some of us have access to the internet in our pockets.
They still own the systems. They still make the rules. But the rules have to balance different constituencies including users and stockholders. Budgets are bigger, but there’s still a limited amount of money to go around. Decisions have to be made. These decisions translate into what traffic the ISP allows on the network. Those decisions are implemented by the employees. Sometimes they screw up. Sometimes they overstep. Sometimes they do the wrong thing. Implementation is hard and one of the things I really push with my clients. Make sure processes do what you think they do.
A long way of dancing around the idea that individual people can make policy decisions we disagree with on their networks, and third parties have no say in them. But those policy decisions need to be made in accordance with internal policies and processes. People can’t just randomly block things without consequences if they violate policies or block things that shouldn’t be blocked.
Ironically, today one of the major telcos managed to accidentally splash their 8xx number database. 8xx numbers are out all over the country while they search for backups to restore the database. This is business critical for thousands of companies, and is probably costing companies money right and left. Accidents can result in bigger problems than malice.
 

Read More